Let's connect
All work

01 · Work · Offscan

Offscan.

Offscan is a source-code security scanner that never sends your code anywhere. Everything, including the AI, runs on your own machine.

Role
Founder · ThreatScope
Team
Solo
When
March 2026 to now
Status
Private release, v0.2.1
Stack
  • JavaScript on Node
  • Babel parser
  • Own taint engine and code graph
  • Ollama, qwen3-coder
  • Single binary via Bun
  • SARIF output
FIG. 02 · The walkthrough, 90 seconds, with sound
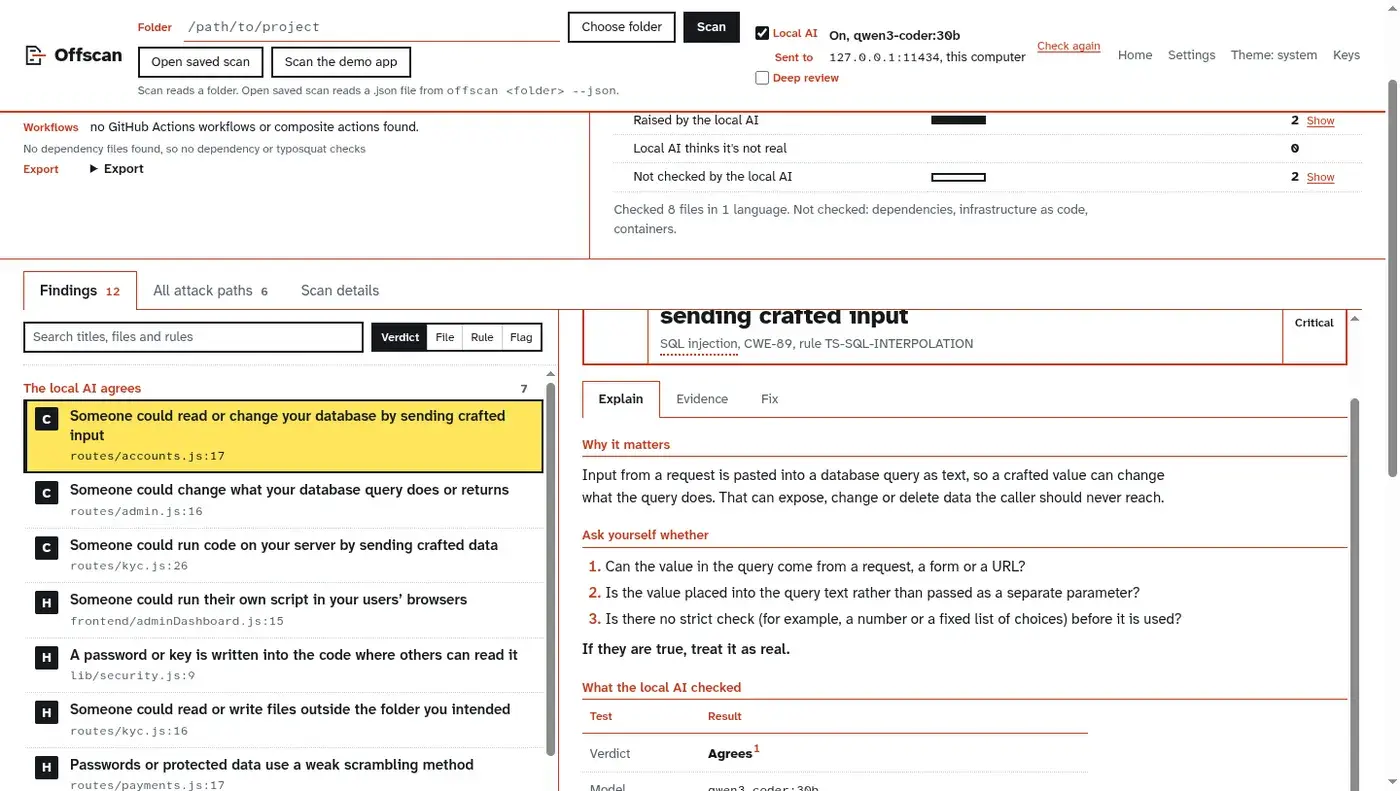
Offscan local dashboard: findings list on the left, a finding explained on the right, sending only to 127.0.0.1 on this computer.
FIG. 03 · The dashboard
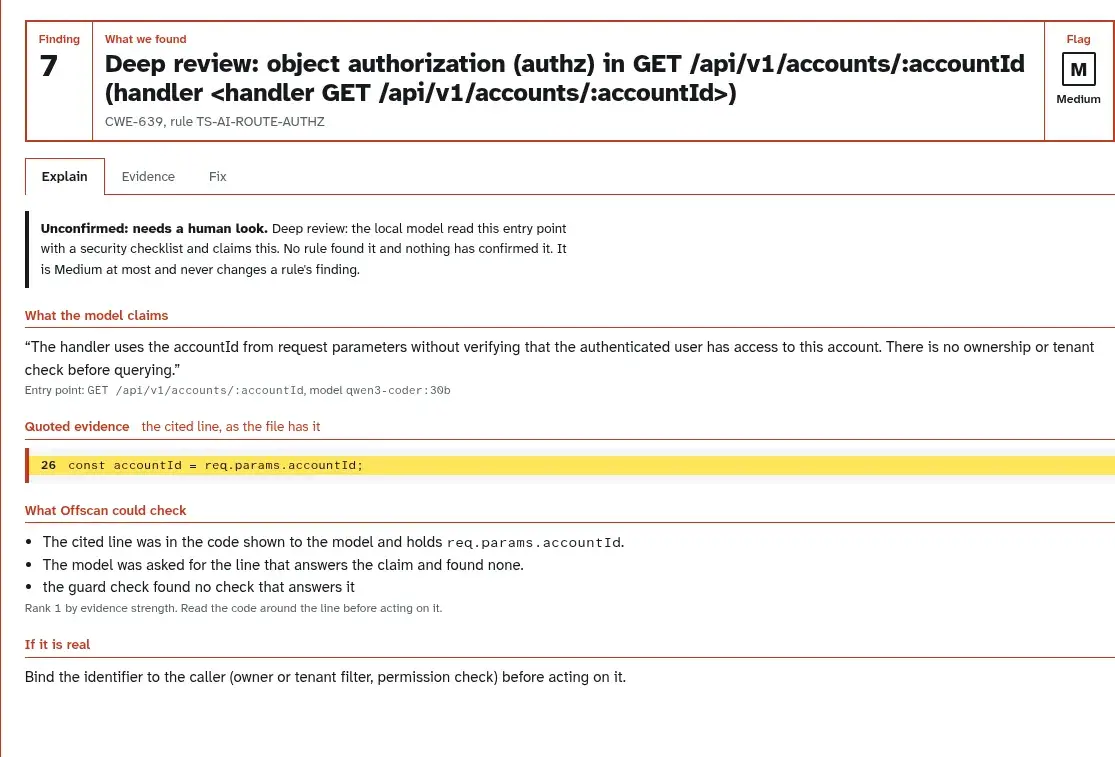
Offscan deep-review panel where the on-device model explains one finding, quotes the exact line, and suggests a fix.
FIG. 04 · Deep review

Esc or click to close

4,600+
automated tests
1,180
commits since July 2026
0
lines of your code sent anywhere
$ offscan demo/bharatpay-payments --no-ai
# 10 findings, 4 attack paths, 0.39 s
A real run on the demo app: offline, no AI.

02 · Story

The story.

  1. The problem

    Your AI wrote it. Nobody read it.

    AI tools now write a lot of the code that ships, and nobody reads all of it. The scanners that could check it run in the cloud: to use them, you hand over your source code. For a bank, or anyone with code they cannot share, that ends the conversation.

  2. Why I built it

    I needed it on my own bug bounties.

    Security is my field. The AI tools I tried on bug bounties flagged too much that was not real, and never connected one bug to the next. I wanted a scanner that checks its own findings, links them into real attack paths, and never sends code anywhere. It started as a hackathon win in spring 2026, and I kept going.

  3. The hard part

    Two designs failed. Then selling it was harder.

    The first design drowned the model in context. The second hit the 4GB limit of my laptop GPU. In June I rebuilt it from scratch. After a LinkedIn post, a vice president at a major Indian card issuer reached out, then went quiet. Banks were my first market, but their sales cycles were too long for a founder with no funding, so in September I turned to developers. Most cold outreach got no reply. A US investor said it was too early and asked to keep the door open. I nearly quit more than once.

  4. Where it is now

    A private release, headed for developers.

    Offscan is in private release, built and tested by one person, and I am taking it to developers.

Who stays in controlYour code, your machine, your call. The AI runs on your own computer, and nothing is sent anywhere.

03 · How it works

How it works.

  1. Read the code

    Its own static analysis and follow untrusted input through the codebase.

  2. Check each finding

    An model gives a second opinion on every serious finding and explains why. It never hides one or changes its severity.

  3. Connect the dots

    Related findings are joined into , so you see how small bugs combine into a real risk.

Ships as

  • One binary per OS
  • Command line
  • Local dashboard
  • GitHub Action with
  • Coding-agent setup

04 · Features

What it does.

  • The classic flaws

    Injection, SSRF, XSS, XXE, path traversal, unverified JWTs and weak hashing.

  • Secrets, masked

    Keys and tokens, even in git history.

  • Supply chain

    Risky Actions and vulnerable dependencies, checked offline.

  • AI-era files

    CLAUDE.md, Cursor rules and MCP configs.

05 · Scenarios

Where it's used.

  1. A solo developer

    Before launch.

    Checks AI-written code without it leaving the laptop.

  2. A team under NDA

    Code that cannot leave.

    Runs fully offline, for banks and client code.

  3. A coding agent

    Scanning its own edits.

    Fixes critical findings before it calls a task done.

Let's connect.

I am not looking for work. I am looking for good people to know.

Index

  1. 1Home
  2. 2Work
  3. 3Security
  4. 4About