Let's connect
All work

01 · Work · bbctl

bbctl.

bbctl is a command line tool I built to run my authorized work from end to end. It organizes , keeps track of what has been checked, and turns findings into a clean report.

It is a personal tool for my own Bugcrowd engagements. Everything runs through one scope-checked gateway, and nothing is ever submitted without me.

Role
Security tooling
Team
Solo
Stack
  • Python
  • Click
  • Textual
  • YAML
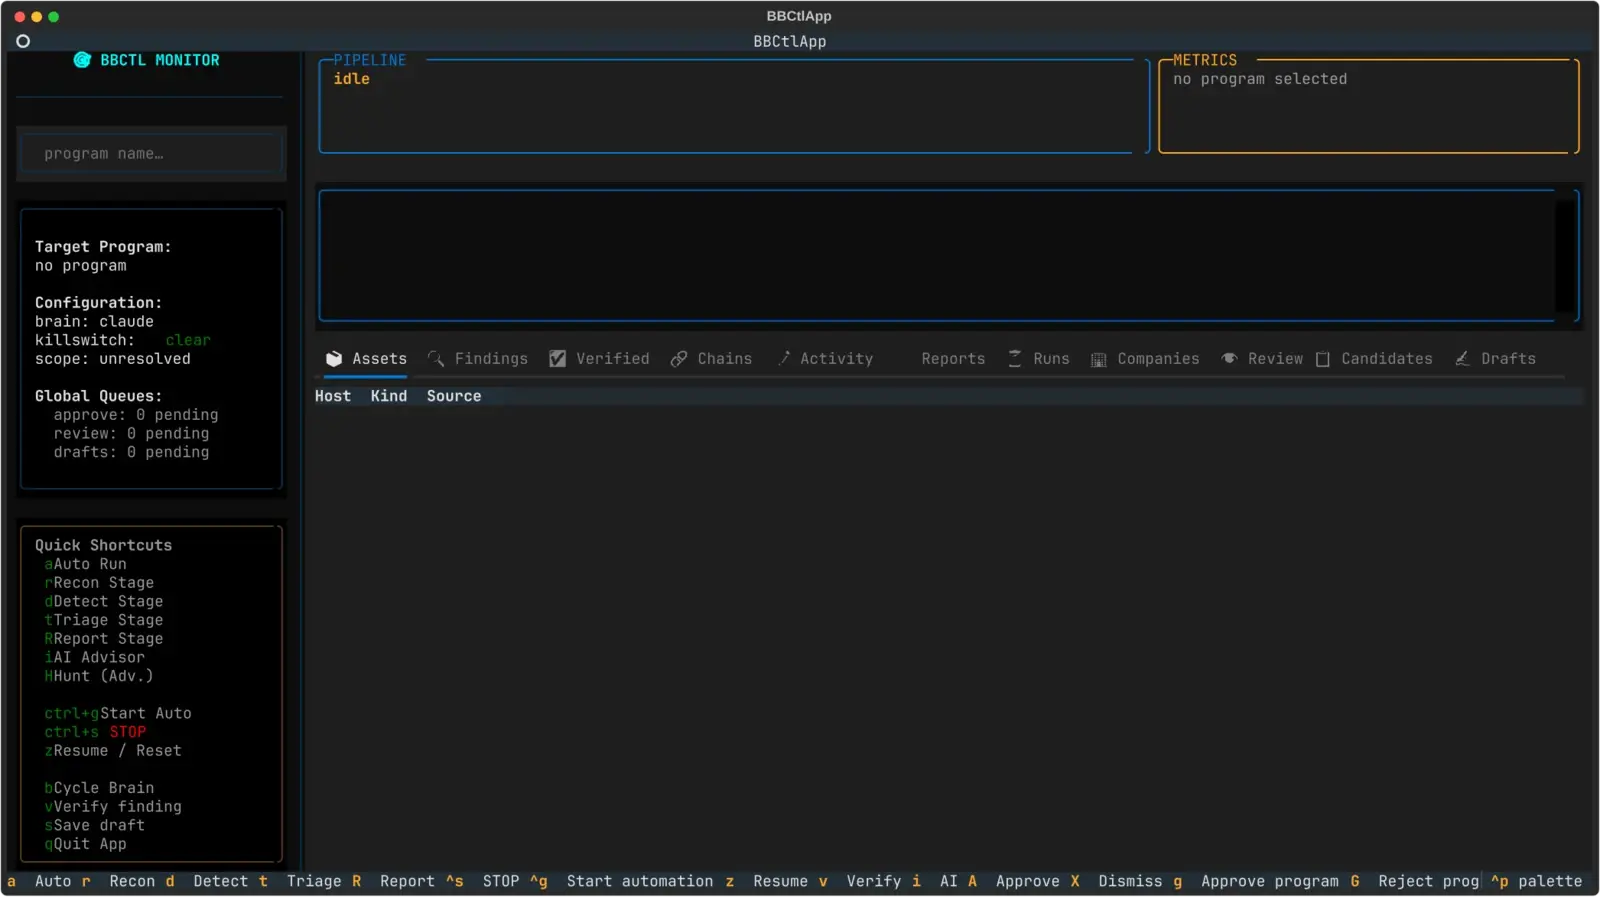
The live bbctl terminal interface: a sidebar with the target program, configuration (AI brain, killswitch, scope) and keyboard shortcuts; pipeline and metrics panels; and tabs for assets, findings, verified items, chains, reports and drafts.
FIG. 02 · The live TUI, idle: target, pipeline, AI brain, and the stage tabs

Esc or click to close

619
automated tests
277
commits
33
commands

02 · Story

Why it exists.

  1. Why I built it

    Bug bounty work is mostly bookkeeping.

    What is in scope, what was checked, what is left, what to report. I wanted one tool that keeps all of it straight for my own authorized engagements.

Who stays in controlAuthorized programs only. One gateway enforces scope, and nothing is submitted without me.

03 · How it works

How it works.

  1. Recon inside scope

    Subdomain search starts only from in-scope wildcards; exact hosts are checked directly and never expanded.

  2. One gateway

    Every tool call passes one gateway that checks scope, the allowlist, the kill switch and the rate limit.

  3. Triage

    Findings are rated on Bugcrowd's public severity scale, and a noise gate marks scanner junk without deleting it.

  4. Draft, never submit

    Only findings I have verified become drafts with proof and repro steps. Drafts are saved, never sent; I press submit.

04 · Features

What it does.

  • Scope is the boundary

    An out-of-scope match always wins, nothing runs without an in-scope match, and a target hiding a second host is refused.

  • Allowlisted tools

    Only tools named in a config file can run at all.

  • Polite by default

    A per-program rate limit, half a request a second by default, kept on disk across restarts.

  • A full audit trail

    Every allowed run, every denial and every timeout is logged per program.

  • Secrets stripped

    Credentials are removed from evidence before it is stored.

  • Capped AI spend

    Daily and per-program limits on AI use; the pipeline itself costs nothing to run.

05 · Scenarios

Where it's used.

  1. A new authorized program

    Loading the scope.

    From the first command, the gateway refuses anything outside it.

  2. An interrupted night

    Picking up again.

    The run resumes from where it stopped, without redoing finished work and with the rate limit intact.

  3. Report day

    From noise to a draft.

    The noise gate trims scanner junk, I verify what is left, and a rated draft waits for my submit.

  4. A self-audit

    What was sent where.

    The audit log shows every request made and every one that was blocked.

Let's connect.

I am not looking for work. I am looking for good people to know.

Index

  1. 1Home
  2. 2Work
  3. 3Security
  4. 4About